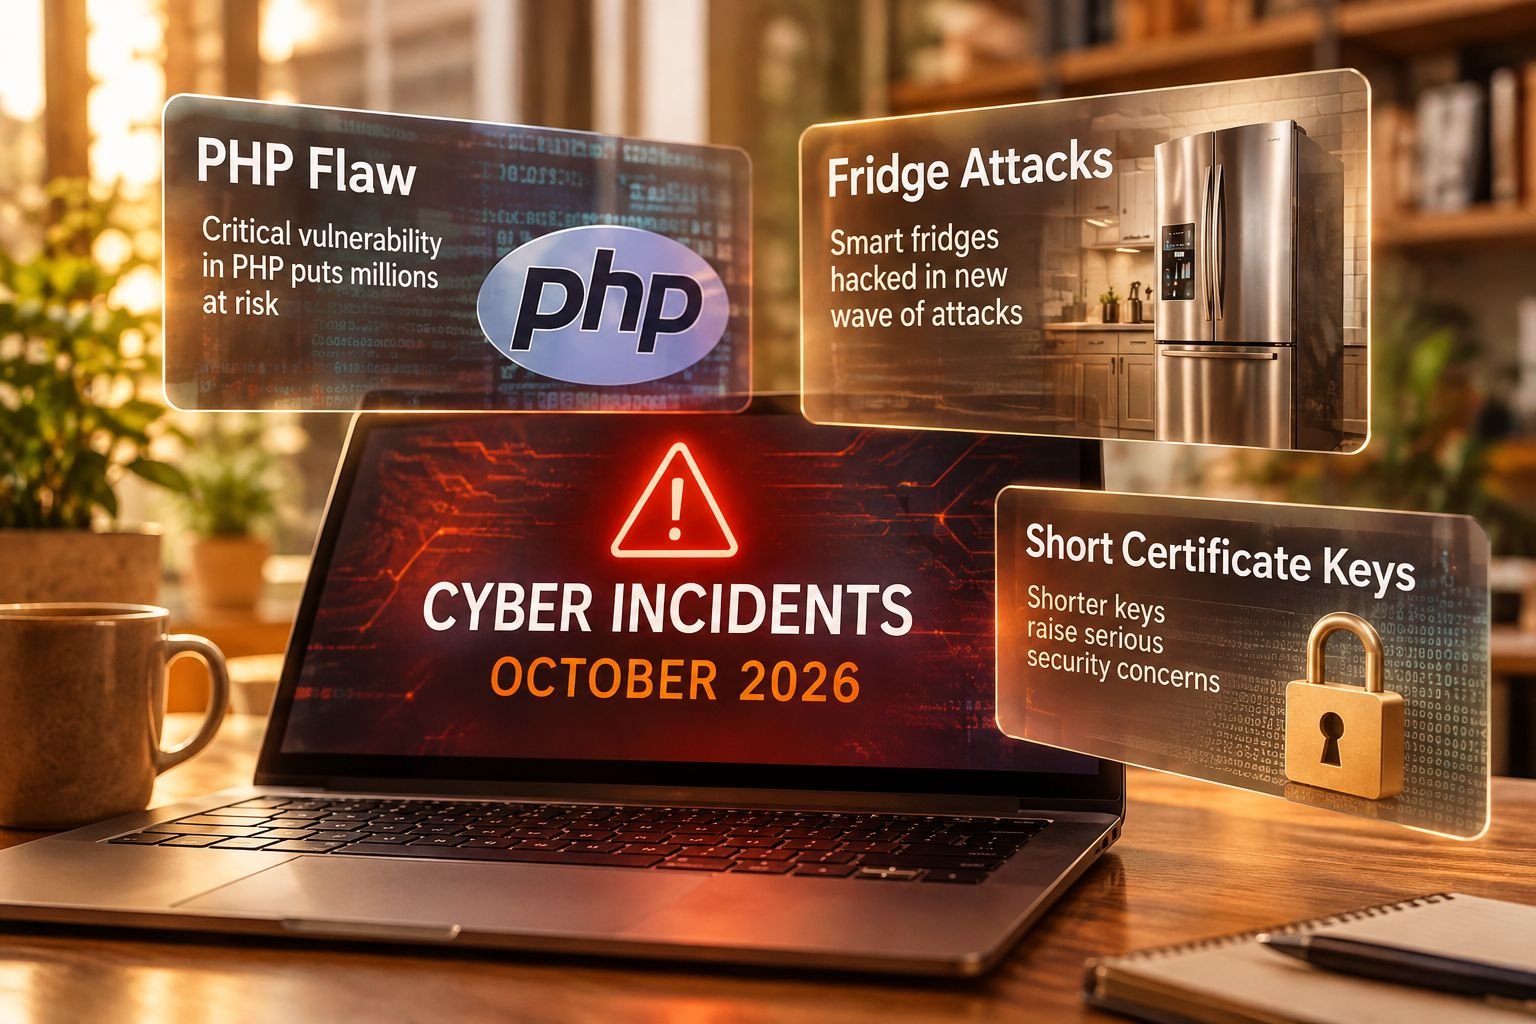
In one month, a flaw in the software behind much of the web, a wave of hacked supermarket freezers and a certificate secured by the number 4 showed the same thing. Attackers now find weak spots faster than most businesses fix them. Here is what happened, and what a small business can do about it this week.
What Changed in October
Security commentators have nicknamed October 2026 “Black October”. The cause is not a single super-virus. AI tools have made it cheaper to find software flaws and to turn them into working attacks, and the gap between a fix being published and criminals exploiting it is shrinking. A Rapid7 threat update puts that gap at around three days.
The weakness is rarely clever. It is the unpatched server, the connected device nobody remembers and the supplier nobody questioned. Three incidents show how.
Incident One: The PHP Flaw
What happened. PHP is the language behind a large number of websites, including WordPress, Drupal and Joomla. Researchers using frontier AI models found two critical flaws in its core (CVE-2026-109618 and CVE-2026-109619) in August. Some security firms say they let an attacker run commands on a server with no login. Details leaked on 20 October, before a fix existed. PHP released patched versions on 21 October, and a security firm saw attacks in the wild that same day. On 26 October the US agency CISA listed both flaws as actively exploited.
Singapore’s Cyber Security Agency (CSA) told organisations to find every system running PHP and patch, internet-facing systems first. In fairness, early reports say the flaws are hard to turn into reliable attacks, and millions of attempts have produced few confirmed breaches. That is a lucky break, not a plan.
What to do.
- Ask whoever runs your website which PHP version it uses and when it was updated. If it is WordPress, the answer matters.
- Patch internet-facing systems first. Where you cannot patch at once, a web application firewall may buy time, as CISA notes.
- If a server was exposed before patching, treat it as possibly compromised and have it checked. Do not assume the patch erased an earlier intrusion.
Incident Two: The Freezers
What happened. On 12 October, attackers remotely took over refrigeration systems at hundreds of supermarkets and independent stores across France. On 2 November it happened again in Sweden, Belgium, Luxembourg, Ireland and Estonia. One Swedish store found its freezers set to 50°C. Stock was thrown away. The reports we reviewed do not say how the attackers got in, but they do show that these systems were reachable from the internet.
What to do. Whatever the route in, the defences are the same.
- List every device that connects to the internet: cold rooms, air-conditioning, CCTV, door access, printers, routers. Include anything a supplier installed.
- Change default passwords and turn off remote access you do not use.
- Keep these devices on a separate network from your office computers and payment systems.
- Know the manual fallback. If the cooling is hacked at midnight, who checks the stock and how?
Incident Three: The Key That Was “4”
What happened. On 17 October, a researcher scanning public certificate data found that eight certificates issued by eMudhra, an Indian certificate authority, used private keys so small they could be guessed in an instant. One key was the number 4. Certificate authorities are the bodies that browsers trust to vouch that a website is genuine, so a forged certificate could let an attacker impersonate a real site. Mozilla, Google and Apple moved to block the certificates, and eMudhra revoked them. It blamed a bug in a key-generation script from April 2025, so the flaw sat unnoticed for about 18 months. AI did not find this one. A person did.
What to do. You cannot audit a certificate authority, but you can limit the damage.
- Keep browsers, operating systems and server software on automatic updates. That is how revocations reach your devices.
- Be aware that some software carries its own list of trusted certificates and may never check revocation. Ask your IT provider about the tools your business depends on.
- Ask suppliers what they do when a security component they rely on fails, and how fast they will tell you.
The Pattern
Across all three, the same three habits separate the businesses that cope from those that do not.
- Patch fast. Days, not months. Retire anything that no longer receives updates.
- Know what is connected. You cannot protect a device you have forgotten. Former CISA director Chris Krebs has urged smaller companies to scan for weaknesses constantly and to patch or take legacy systems offline.
- Test your suppliers. Most SMEs run on other people’s software. Their weakness becomes yours.
AI cuts both ways. The same tools that speed up attackers can help you check your own systems. Security specialists quoted by Axios urge companies to test their own defences proactively, before someone else does.
Where the Law Fits In
Security is also a legal duty. The Personal Data Protection Act 2012 requires reasonable security arrangements for personal data (section 24), and “reasonable” rises with the threat. The PDPC fined People Central Pte Ltd and Singapore Data Hub Pte Ltd S$17,500 each for security failures in decisions announced in early 2026. If a breach is notifiable, you must tell the PDPC within three calendar days of concluding that it is. A written breach plan and tight supplier contracts will serve you well on both counts. We are glad to help with either.
Your 30-Day Checklist
- List everything connected to the internet, including supplier-installed devices.
- Ask your website and IT providers in writing what they patched after 21 October.
- Set automatic updates, and replace unsupported equipment.
- Replace default passwords and switch on multi-factor authentication for email, cloud and admin accounts.
- Separate cameras, cooling and other devices from your main network.
- Write a one-page incident plan: who decides, who calls the PDPC, who speaks to customers.
- Subscribe to CSA’s alerts so the next warning reaches a person.
The Bottom Line
None of these incidents needed a master criminal. They needed an unpatched server, a connected freezer and a script bug. AI means the next set of gaps will be found sooner. The businesses that do the basics now will be the ones still trading when it happens.
OTP Law Corporation advises Singapore businesses on cybersecurity obligations, PDPA compliance, breach response and technology contracts. If you would like a practical review of your position, contact us.
This article is for general information only and is not legal advice. Please speak to a lawyer about your specific situation.


